Anthropic says new safeguards sharply reduce AI distillation attacks
Anthropic announced new safeguards have reduced data harvested in AI distillation attacks against its Claude models by 90% to 99%. The company stated that the number of reasoning tokens extracted by distillers is now 10 to 100 times lower, citing Chinese AI startup Z.ai as an example of a firm that attempted to distill capabilities.
Anthropic's reported success in sharply reducing distillation attacks highlights a growing concern for leading AI developers. The practice, which involves copying advanced AI capabilities, is seen by companies like Anthropic, OpenAI, and Google as enabling rivals to reproduce sophisticated models more quickly and at a lower cost. This issue gains particular urgency amid intensifying US-China competition in the AI sector, where firms aim to protect proprietary model development.
The new safeguards primarily target Claude's reasoning processes, restricting access and making it harder for attackers to use proxy networks for repeated probes. Anthropic claims its safety system is "roughly as robust as those that prevent Claude from helping build bioweapons" and has "a false positive rate of less than 0.1%". This suggests a technical approach focused on making the extraction of core AI logic significantly more difficult, rather than simply blocking access.
By identifying and banning tens of thousands of accounts linked to these campaigns, Anthropic demonstrates an active enforcement strategy. The specific mention of Z.ai (Zhipu) and its GLM-5.3 model development illustrates the direct competitive implications. Anthropic warned such practices pose safety and national security risks, indicating that AI firms are prepared to attribute alleged distillation efforts publicly.
Share this article
Related reading
6 stories
Meta says its new AI models on par with OpenAI, Anthropic
Meta also claims its new AI models are on par with OpenAI and Anthropic, intensifying the competitive landscape.
Meta releases Muse Wonder AI models to challenge Anthropic and OpenAI
Meta's Muse Wonder AI models were released to challenge established players like Anthropic and OpenAI.
Mastercard Expands APAC Dining Programme to 1,300 Restaurants
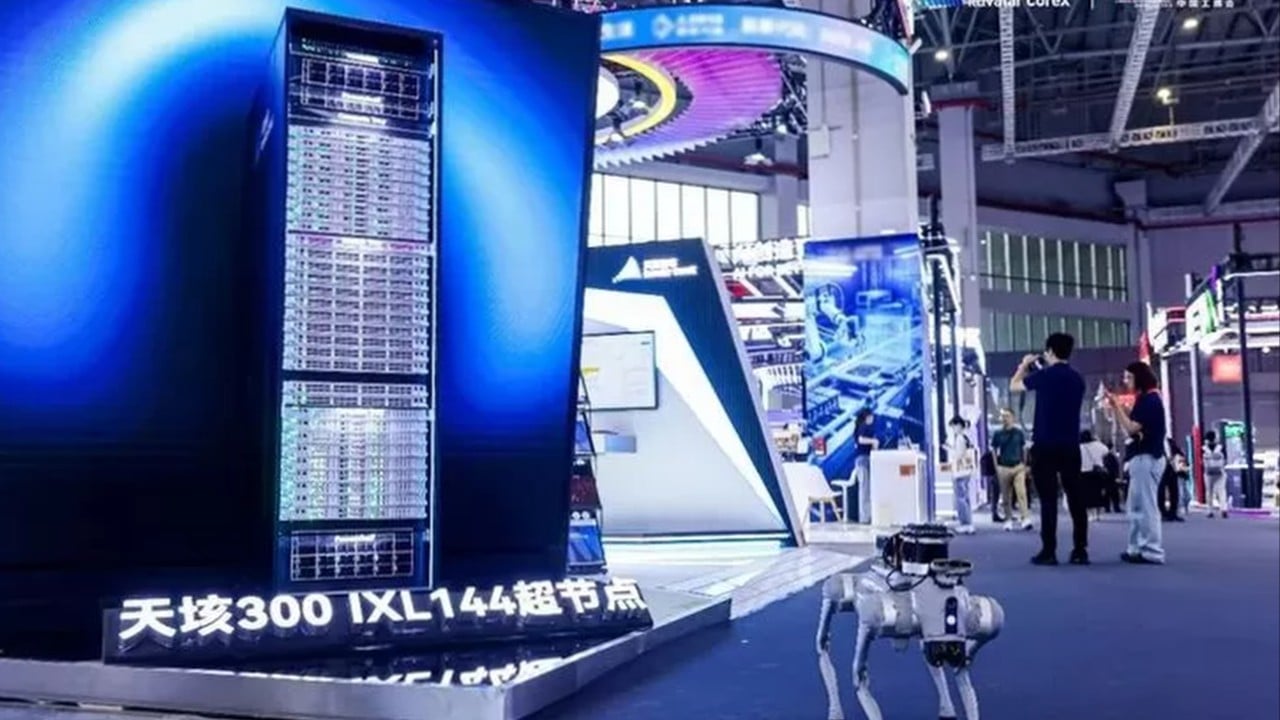
China’s Iluvatar CoreX’s first AI computing supernode squeezes most GPUs in 1 system
FIS Launches Agentic AI Tool for CFOs to Spot Cash Flow Risks Earlier