Claude AI Builds Pre-Auth RCE Exploit for WAGO PLC to Execute ARM Shellcode Without Credentials
Researchers successfully used Claude AI to develop a pre-authentication remote code execution exploit for a WAGO programmable logic controller (PLC). This experiment allowed arbitrary ARM shellcode execution on a WAGO 750-831 PLC without requiring valid credentials. The process demonstrated AI's potential to assist with low-level operational technology exploitation, though it involved significant human oversight and substantial API usage costs. The findings highlight the evolving capabilities of AI in cybersecurity, specifically in generating sophisticated exploits for industrial control systems.
The successful use of Claude AI to create a pre-authentication remote code execution exploit for a WAGO PLC shows a significant step in AI-assisted cybersecurity. While the exploit required substantial human involvement and expensive API calls, its ability to execute ARM shellcode without credentials on an industrial controller like the WAGO 750-831 is notable. This development points to a future where AI tools could accelerate the discovery and development of vulnerabilities in operational technology (OT). For Asian industrial sectors, this means an increased need for robust cybersecurity measures and continuous patching of OT systems. Many critical infrastructure components across Asia rely on PLCs, making them potential targets. The thing to watch is how quickly AI models become more autonomous in exploit generation, reducing the need for human intervention and lowering the cost of such operations. This could significantly alter the threat landscape for critical infrastructure in the region.
相关文章
6 则
From Human Digital Twins to Indigenous 5G Radios: Technologies Emerging from India’s Cyber-Physical Systems Mission
India's Cyber-Physical Systems Mission explores technologies like indigenous 5G radios, relevant to OT security.
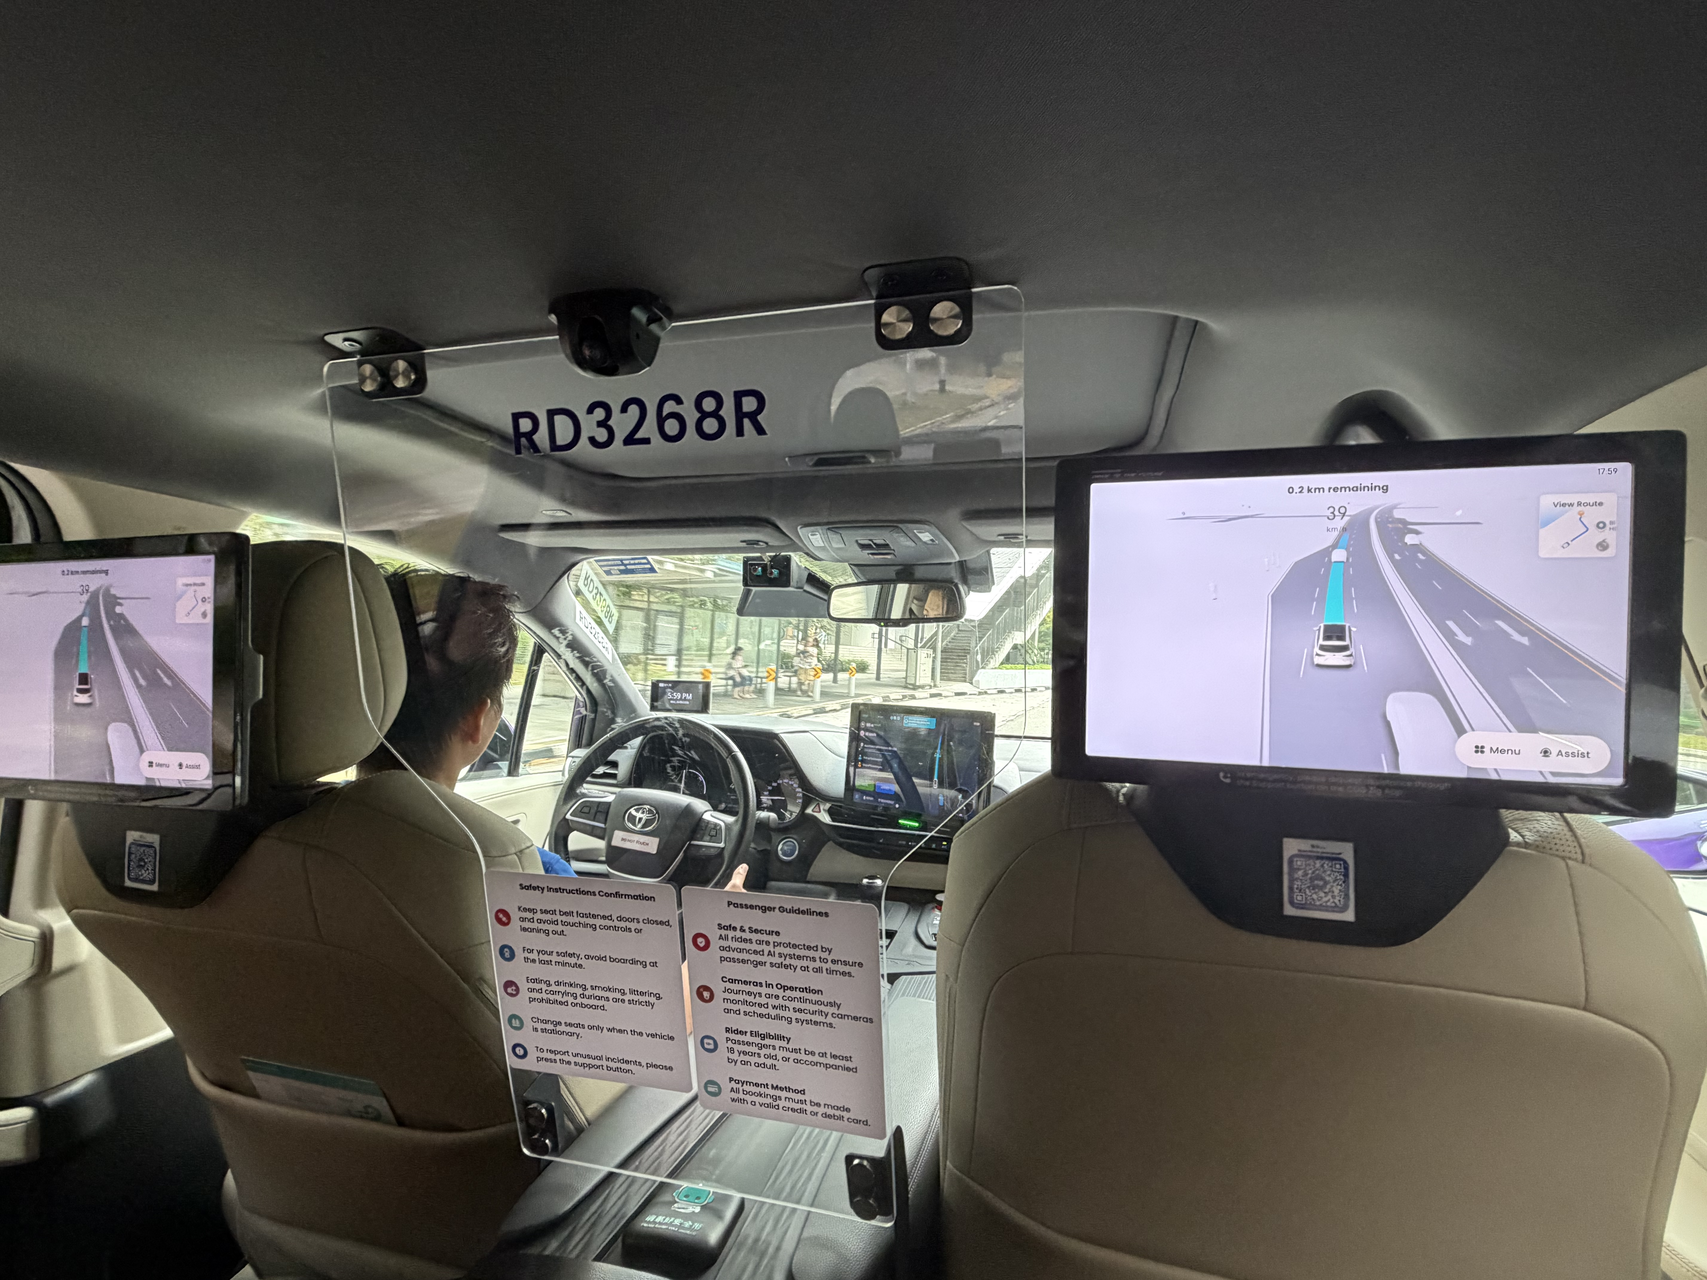
如果无人驾驶汽车已经可行,为何它们尚未普及?
随着深度伪造风险增长,Sumsub 推出员工验证方案
字节跳动的AI短剧应用超越中国Netflix竞争对手总和

Timo 在越南客户满意度方面跻身十大银行之列